
Connect applications, devices, and AI agents without exposure.
Atsign Platform securely connects field equipment to monitoring applications, AI agents to approved data services, and support teams to equipment at customer sites. You control which connections are allowed and keep the data they exchange private.
It is the foundation behind Atsign EdgeAI, NoPorts, and custom-built applications. These shared capabilities help teams reduce exposed attack surface, deploy faster, and manage communication permissions as requirements change.
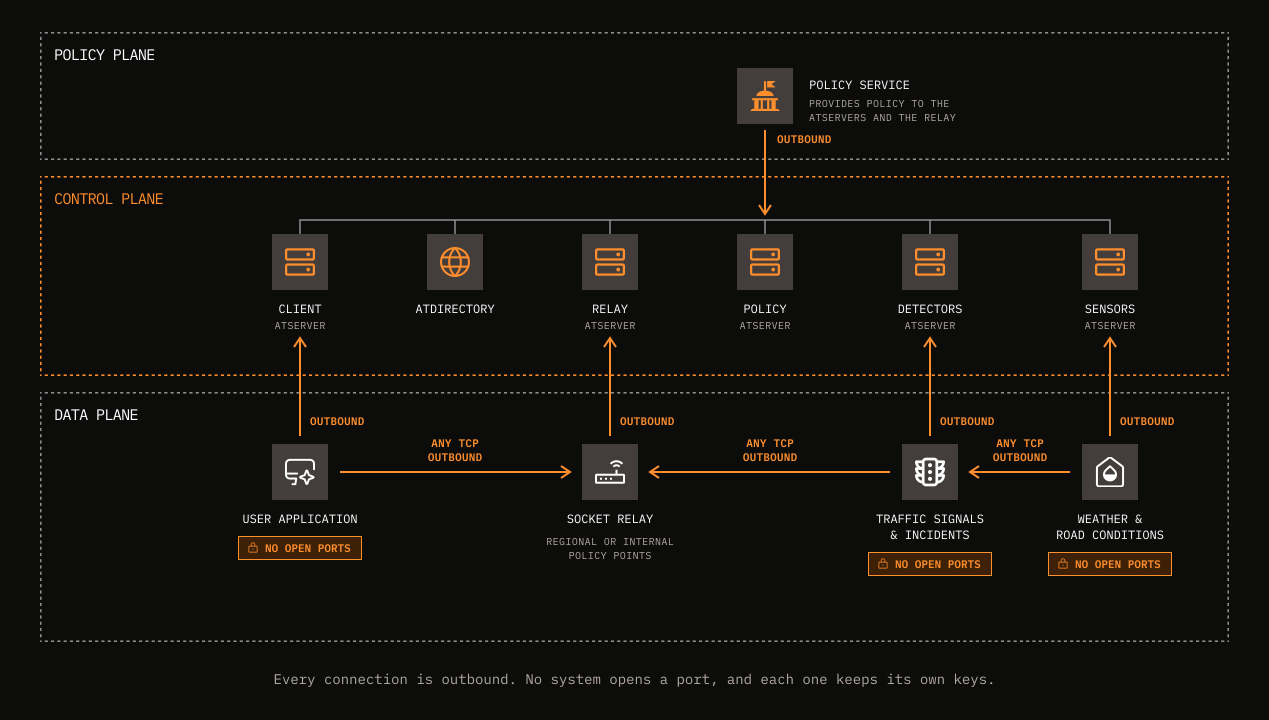
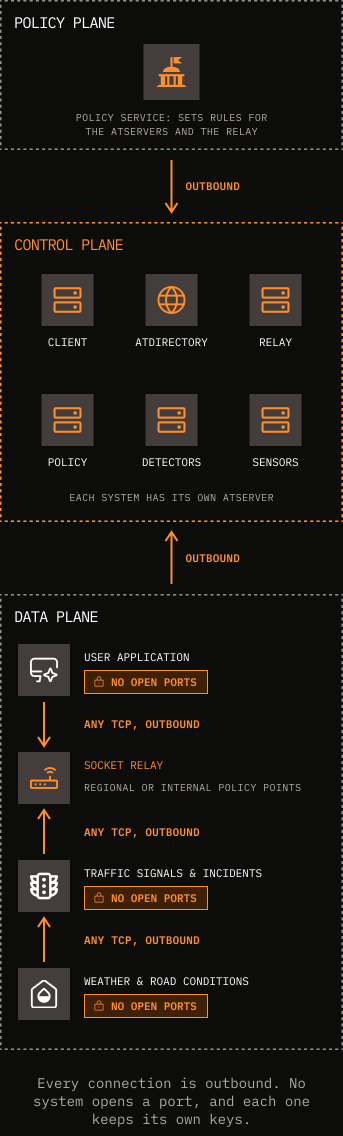
How Atsign protects connected systems
Authentication, communication permissions, and encryption work together to protect these connections across networks.
[01]
Verify before granting access
Devices, applications, services, and agents authenticate using cryptographic identities before gaining access to protected resources. Their communication permissions remain consistent when IP addresses or network locations change.
[02]
No exposed inbound connections
Protected applications and devices initiate connections outward. They can communicate with authorized services without opening inbound listening ports or exposing protected services to public discovery.
[03]
Communication you control
Access is never all-or-nothing. Policy-based rules define which devices, applications, and agents can communicate and which resources they can access. Update permissions as requirements change, or use a granular Kill Switch to restrict or revoke communication when needed.
[04]
Encryption and crypto agility
Protected communications are encrypted end to end. Crypto agility lets you update cryptographic methods as standards and threats evolve. Post-quantum cryptography helps protect sensitive communications against future quantum-computing threats.
[05]
Private keys under your control
The private keys needed to decrypt communications remain under the control of the communicating devices and applications. Atsign and network intermediaries do not hold those keys and cannot decrypt the protected content.
[06]
Connect across networks
Deploy equipment on a customer’s network, use cellular connectivity at a remote site, or connect applications running in different clouds. Communication permissions remain independent of network addresses and locations.
How Atsign fits into your environment
Add secure communication and control while continuing to use your chosen applications, infrastructure, and AI models.
Where it fits
Use Atsign EdgeAI for secure connectivity and integrated management across distributed deployments or Atsign SDKs to build the platform’s capabilities into your own applications.
What it reduces
Reduce dependence on exposed inbound services, VPN provisioning, site-specific firewall changes, and repeated network configuration. Spend less time arranging access across environments and administering one-off connections.
What stays the same, and what changes
Build on your existing applications and infrastructure. Teams add endpoint software or integrate Atsign SDKs, then configure communication permissions to fit the deployment. The implementation is tailored to your systems and operating requirements. Networks that restrict outbound connections may require allowlisting.

Build secure communication into your applications
Atsign SDK
Use Atsign SDKs to add secure connectivity, communication permissions, and private data exchange to applications, devices, and AI agents. Explore the documentation and sample applications to see how the platform works.
Atsign AI Architect
For a guided development approach, Atsign AI Architect helps you map application components, permissions, and communication paths. It turns that blueprint into structured guidance for your AI coding assistant.
Validate the architecture
Review how Atsign fits your applications, networks, and security requirements.
Speak to a core engineer
Discuss your deployment, communication policies, cryptographic key management, or integration requirements with our engineering team. We’ll work through the architecture and what implementation would involve.
Schedule a technical validation callExplore the technical documentation
Review the platform architecture, SDKs, and open-source implementation. Use the documentation to assess how authentication, communication permissions, and encryption fit into your solution.
Read the technical documentation


